ISO/IEC 27005 Risk Manager – eLearning
Develop the knowledge and skills needed to identify, analyse, evaluate, treat and communicate information security risks based on ISO/IEC 27005. The course introduces key risk management concepts and principles and shows how they can be applied to establish and improve information security risk management within an organisation.
Order e-learning course here
The course provides a structured introduction to information security risk management based on ISO/IEC 27005 and ISO 31000. You will learn how to establish the context for risk management, identify and analyse risks, evaluate their significance and determine appropriate risk treatment.
The course also covers risk communication, monitoring and reporting, as well as several established risk assessment approaches, including OCTAVE, MEHARI, EBIOS, NIST, CRAMM and Harmonized TRA.
The training is delivered through the myPECB platform and combines video based learning with course materials, practical examples and quizzes.
 What will you get out of the course?
After completing the course, you will be able to:
- Explain the risk management concepts and principles outlined in ISO/IEC 27005 and ISO 31000
- Establish, maintain and improve an information security risk management framework
- Apply information security risk management processes based on ISO/IEC 27005
- Identify, analyse and evaluate information security risks
- Determine and apply appropriate risk treatment
- Plan and establish risk communication and consultation activities
- Monitor, review, record and report information security risks
- Understand different information security risk assessment methods
 Who is this course for?
The course is suitable for:
- Managers and consultants involved in or responsible for information security
- Professionals responsible for managing information security risks
- Members of information security teams
- IT professionals and privacy officers
- Professionals responsible for maintaining conformity with ISO/IEC 27001 information security requirements
- Project managers, consultants and advisors who want to develop expertise in information security risk management
 Prerequisites
There are no formal prerequisites for this course.
 Course content
The course covers:
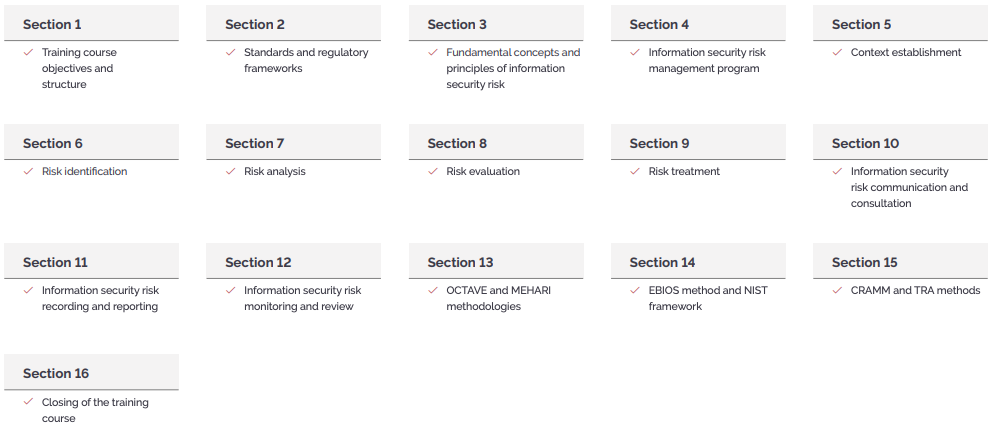
- Training course objectives and structure
- Standards and regulatory frameworks
- Fundamental concepts and principles of information security risk
- Information security risk management programme
- Context establishment
- Risk identification
- Risk analysis
- Risk evaluation
- Risk treatment
- Information security risk communication and consultation
- Information security risk recording and reporting
- Information security risk monitoring and review
- OCTAVE and MEHARI methodologies
- EBIOS method and NIST framework
- CRAMM and TRA methods
Training course structure
 Exam and certification
Exam
After completing the course, you can take the PECB Certified ISO/IEC 27005 Risk Manager exam.
The exam covers four competency domains:
- Fundamental principles and concepts of information security risk management
- Implementation of an information security risk management programme
- Information security risk management framework and processes based on ISO/IEC 27005
- Other information security risk assessment methods
Certification
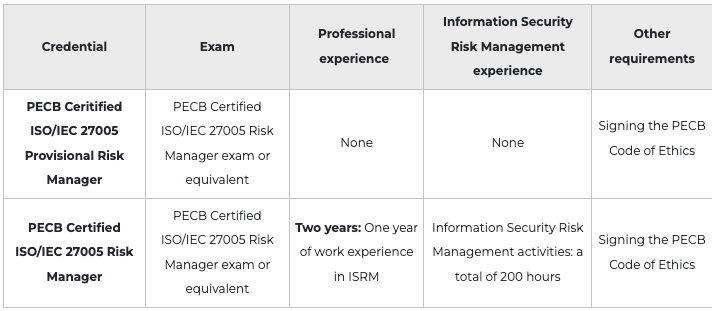
After successfully completing the exam, you can apply for the credentials shown on the table below. You will receive a certificate once you comply with all the requirements related to the selected credential. For more information about ISO/IEC 27001 certifications and the PECB certification process, please refer to the Certification Rules and Policies.