Gain the knowledge and practical skills needed to implement and manage an Information Security Management System (ISMS) based on ISO/IEC 27001. The course provides a comprehensive understanding of the requirements of the standard and how they can be applied to protect the confidentiality, integrity and availability of information.
The course combines theoretical knowledge with practical guidance for planning, implementing, managing, monitoring and continually improving an ISMS. You will learn how to interpret ISO/IEC 27001 in the context of an organisation, assess existing information security practices, define the scope of an ISMS and establish the processes needed for effective implementation.
The training is delivered through the myPECB platform and includes video-based learning, course materials, exercises and quizzes. The course content can be accessed digitally, and the exam can be taken online at a suitable date and time through PECB Exams.
 What will you get out of the course?
After completing the course, you will be able to:
 Who is this course for?
The course is suitable for:
 Prerequisites
There are no formal prerequisites for this course.
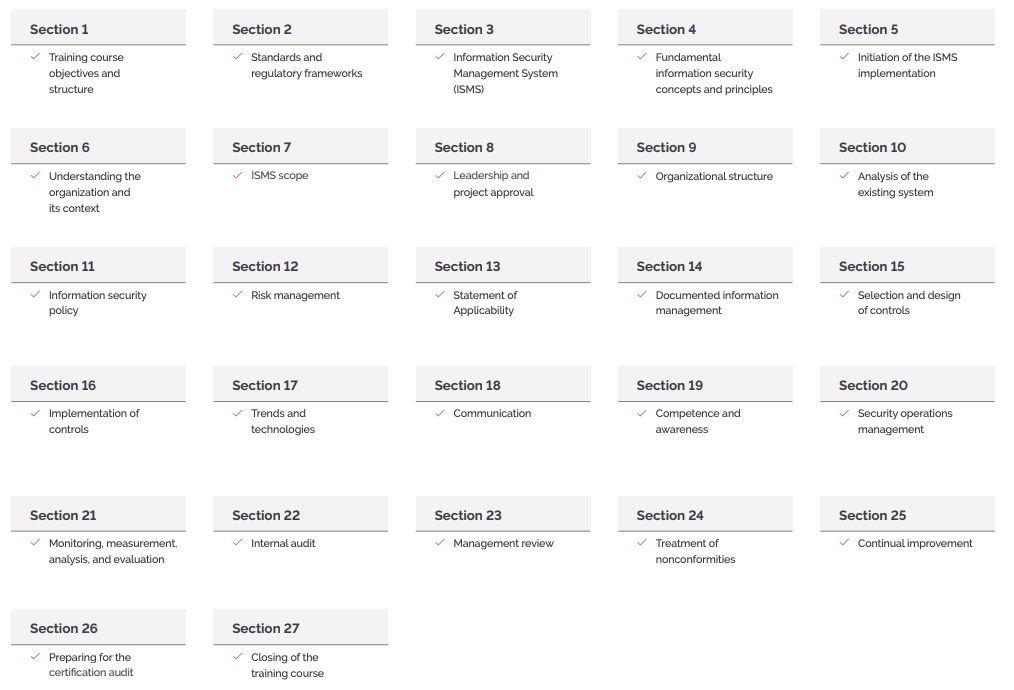
 Course content
 Exam and certification
After completing the course, you can take the PECB Certified ISO/IEC 27001 Lead Implementer exam. The exam covers seven competency domains, including ISMS fundamentals, implementation planning, implementation, monitoring, continual improvement and preparation for a certification audit.
After successfully completing the exam, you can apply for the credentials shown on the table below. You will receive a certificate once you comply with all the requirements related to the selected credential. For more information about ISO/IEC 27001 certifications and the PECB certification process, please refer to the Certification Rules and Policies.