ISO/IEC 27001 Lead Auditor – eLearning

Develop the knowledge and skills needed to plan, conduct and follow up on Information Security Management System audits based on ISO/IEC 27001. The course focuses on recognised audit principles, procedures and techniques and prepares you to manage an audit programme, lead an audit team and assess an organisation’s ISMS.

Order e-learning course here


The course provides a comprehensive introduction to auditing Information Security Management Systems. You will learn how to plan and conduct internal and external audits in accordance with ISO 19011 and the ISO/IEC 17021-1 certification process.

The training also covers evidence-based and risk-based auditing, communication throughout the audit process, documentation of findings and nonconformities, evaluation of corrective action plans and management of an internal audit programme.

The course is delivered through the myPECB platform and combines video-based learning with course materials, exercises and quizzes.
What will you get out of the course?

After completing the course, you will be able to:
  • Understand the operation of an Information Security Management System based on ISO/IEC 27001
  • Understand the relationship between ISO/IEC 27001, ISO/IEC 27002 and other standards and regulatory frameworks
  • Understand the auditor’s role in planning, leading and following up on management system audits
  • Interpret ISO/IEC 27001 requirements in the context of an ISMS audit
  • Plan and conduct internal and external ISMS audits
  • Lead an audit and manage an audit team
  • Document audit findings and prepare audit reports
  • Follow up on audits in accordance with ISO 19011

Who is this course for?

The course is suitable for:
  • Auditors who want to perform and lead ISMS certification audits
  • Managers and consultants who want to develop expertise in ISMS auditing
  • Professionals responsible for maintaining conformity with ISMS requirements
  • Technical experts preparing for Information Security Management System audits
  • Advisors working with information security management

Prerequisites

There are no formal prerequisites for this course.
Course content

The course covers:
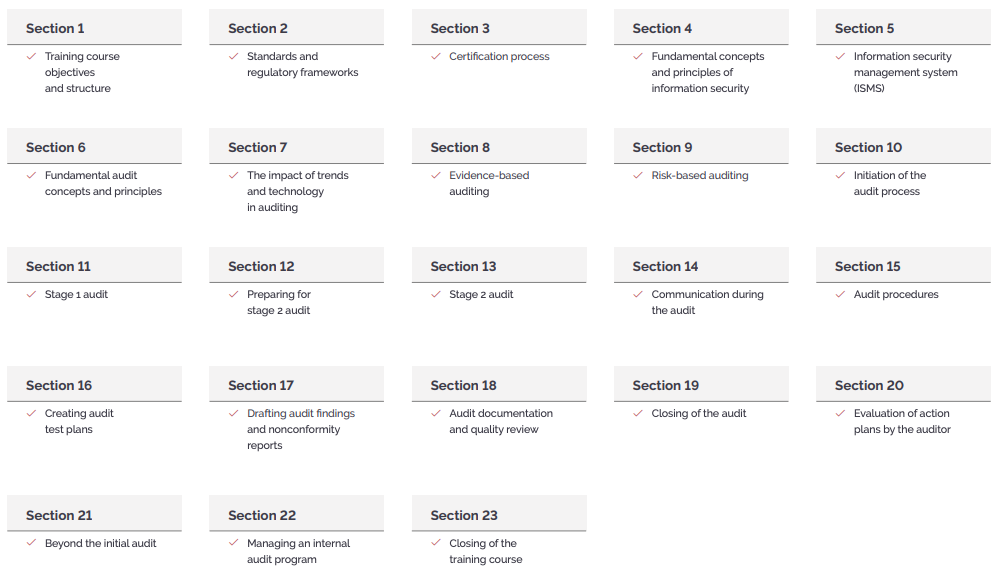
  • Training course objectives and structure
  • Standards and regulatory frameworks
  • Certification process
  • Fundamental concepts and principles of information security
  • Information Security Management Systems
  • Fundamental audit concepts and principles
  • Trends and technology in auditing
  • Evidence-based auditing
  • Risk-based auditing
  • Initiation of the audit process
  • Stage 1 audit
  • Preparation for stage 2 audit
  • Stage 2 audit
  • Communication during the audit
  • Audit procedures
  • Creating audit test plans
  • Drafting audit findings and nonconformity reports
  • Audit documentation and quality review
  • Closing the audit
  • Evaluation of action plans
  • Activities beyond the initial audit
  • Managing an internal audit programme

Training course structure

Exam and certification

Exam

After completing the course, you can take the PECB Certified ISO/IEC 27001 Lead Auditor exam.

The exam covers seven competency domains, including ISMS principles, audit concepts, preparation and conduct of ISO/IEC 27001 audits, closing an audit and management of an ISO/IEC 27001 audit programme.

Certification

After successfully completing the exam, you can apply for the credentials shown on the table below. You will receive a certificate once you comply with all the requirements related to the selected credential. For more information about ISO/IEC 27001 certifications and the PECB certification process, please refer to the Certification Rules and Policies.
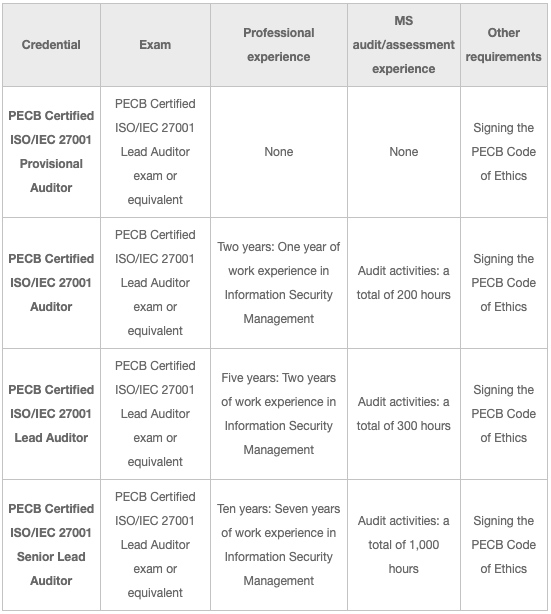
Cetification LA 27001.png